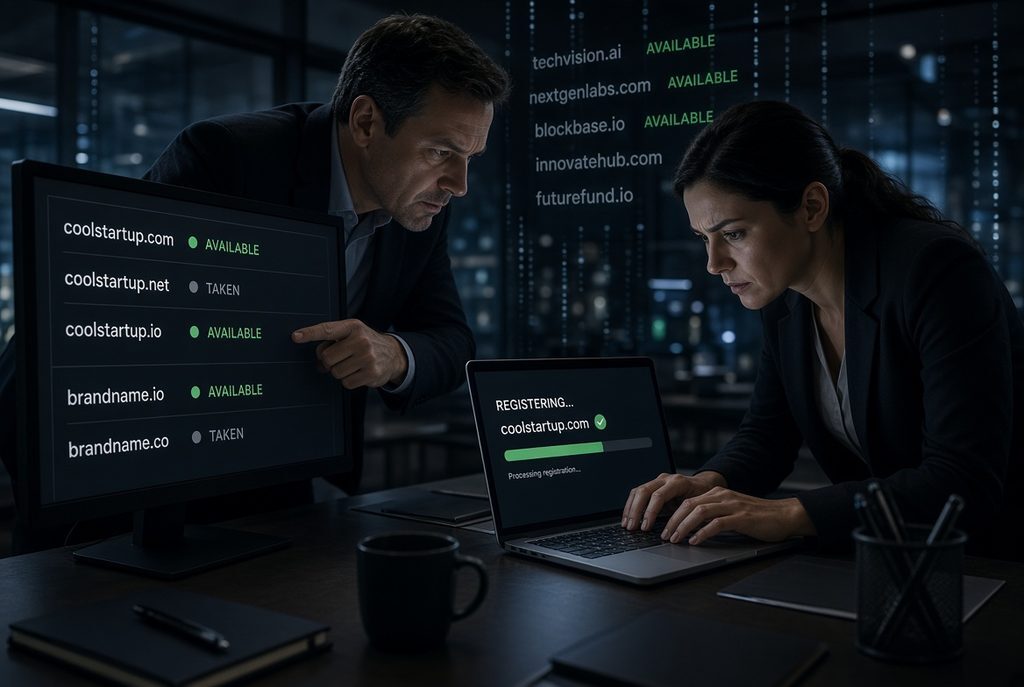
No clear, enforceable contractual wording in the ICANN Registrar Accreditation Agreement (RAA) expressly prevents a registrar from front-running domain name searches conducted on its own website—whether by rogue employees or as a corporate practice. The situation is different (and stronger) on the registry side.
Registrar Accreditation Agreement (RAA)
The current RAA (2013 version, as amended through 2024) does not contain an explicit ban on front-running.
The closest provision is Section 3.7.9:
“Registrar shall abide by any Consensus Policy prohibiting or restricting warehousing of or speculation in domain names by registrars.”
However:
- No such Consensus Policy has ever been adopted. The official list of ICANN Consensus Policies includes items such as the UDRP, transfer policies, Expired Domain Deletion Policy, AGP Limits Policy, Registration Data Marketing Restriction Policy, and others related to data accuracy and marketing restrictions on registration data. It does not include a policy prohibiting warehousing, speculation, or front-running.
- The topics on which Consensus Policies may be developed (in the Consensus Policies and Temporary Policies Specification) include “prohibitions on warehousing of or speculation in domain names by registries or registrars,” but the multistakeholder process has never produced one.
Other relevant RAA provisions (data protection for Personal Data of registrants after registration, restrictions on certain uses of public RDDS/WHOIS data, general obligation to abide by applicable laws) do not specifically address the use of pre-registration availability-search or query logs from a registrar’s own website. Search queries for unregistered names fall outside the typical “Personal Data” protections that apply to existing registrants.
Historical context confirms this gap. ICANN’s Security and Stability Advisory Committee (SSAC) examined domain name front-running in 2007–2008 (SAC 022 and SAC 024). Those reports found insufficient evidence of systematic front-running by parties in the registration process and noted that the agreements did not expressly prohibit monitoring and using availability-check data. Practices such as Network Solutions temporarily reserving searched names were controversial but were not clearly barred by the RAA.
Registry Agreements (Base Registry Agreement)
There is explicit language in Specification 9 (Registry Operator Code of Conduct) of the Base Registry Agreement used for new gTLDs:
Registry Operator will not, and will not allow any parent, subsidiary, Affiliate, subcontractor or other related entity … (each, a “Registry Related Party”), to:
… c. register names in the TLD or sub-domains of the TLD based upon proprietary access to information about searches or resolution requests by consumers for domain names not yet registered (commonly known as, “front-running”);
This prohibition applies to the registry operator and Registry Related Parties (which can include affiliated entities involved in registry services). It also includes related restrictions on preferential treatment of registrars and on disclosure of personal data by affiliated registrars. Exemptions are available in limited cases (e.g., certain brand or closed TLDs meeting specific criteria).
This does not directly regulate a pure registrar’s use of search data from its own retail website, unless the registrar is acting as a Registry Related Party in a given TLD.
Bottom Line
| Scenario | Explicit ICANN contractual prohibition? |
|---|---|
| Registry (or related party) front-running based on search/resolution data | Yes (Specification 9 Code of Conduct) |
| Registrar front-running based on its own website searches (corporate practice or rogue employee) | No clear explicit ban; only a placeholder for a Consensus Policy that has never been created |
| Use of post-registration Personal Data | Protections exist, but these do not cover pre-registration searches |
In short, the RAA contains a placeholder that could have been used to prohibit registrar warehousing/speculation/front-running, but the policy was never developed. Rogue employees or unwritten corporate procedures involving search-data front-running are not clearly barred by the ICANN registrar agreement itself. Any remedy would more likely depend on the registrar’s internal policies, employment contracts, consumer-protection or unfair-competition laws in relevant jurisdictions, or (in limited cases) registry-side rules if affiliation is involved.
This gap has been discussed in the ICANN community for years without resulting in a specific Consensus Policy.